
In April 2026, the International Consortium of Investigative Journalists (ICIJ) released a new investigation detailing what it described as a large-scale digital counteroffensive launched after publication of its “China Targets” series a year earlier. According to the investigation, cyber actors linked to China impersonated ICIJ journalists and supposed whistleblowers while using phishing emails, fake websites, and social engineering tactics to target journalists, Taiwanese political figures, Uyghurs, Tibetans, Hong Kong activists, and others.
The campaign sought to obtain sensitive information and, according to researchers, represents an increasingly sophisticated form of transnational repression. The attacks are being viewed as retaliation for investigative reporting into Beijing’s efforts to pursue critics and dissidents overseas.
Retaliation after the ‘China Targets’ investigation
In 2025, ICIJ and 42 media partners published the “China Targets” investigation, documenting methods the Chinese government has allegedly used to threaten, pressure, and intimidate dissidents abroad. These included Interpol Red Notices, pressure on family members, and cyberattacks. Soon after the investigation was published, people connected to the ICIJ network began receiving suspicious messages.
A joint investigation by ICIJ and the University of Toronto’s Citizen Lab found that attackers impersonated ICIJ journalists and contacted targets through email, LINE, and other communication platforms. They also created fraudulent versions of ICIJ webpages and sent seemingly professional interview requests designed to persuade recipients to click malicious links or disclose sensitive information.
Citizen Lab described the operation as a widespread campaign to obtain private information from people and organizations of interest to the Chinese government. Targets included Taiwanese human rights and political groups, Uyghurs, Tibetans, Hong Kong diaspora activists, and journalists covering those communities.
The attacks relied heavily on spear phishing, combining technical methods with carefully tailored social engineering. Rather than simply sending generic phishing messages, the attackers assumed the identities of real journalists, using their names and professional reputations to establish trust. Some targets were even offered brand-new Samsung smartphones, raising concerns that the physical lures may have been intended to facilitate surveillance or provide another way to access recipients.
Taiwan becomes a major target
Taiwan was one of the campaign’s primary targets, with attackers approaching members of the media, political circles, and civil society organizations. In one case, attackers impersonated Yi-Shan Chen, editor-in-chief of Taiwan’s CommonWealth Magazine.
Kuochun Hung, chief operating officer of the Taiwanese media organization Watchout, received emails and LINE messages from someone claiming to be Yi-Shan Chen. The sender requested interviews on issues including efforts to impeach Taiwan’s president, political divisions between the ruling and opposition camps, and the activities of Watchout and other civic groups. The sender provided a link to a fake ICIJ webpage along with a list of interview questions and even cautioned Hung to “pay attention to information security.”
Hung did not click the link. The sender later asked him about Taiwanese religious organizations and the latest U.S. White House National Security Strategy. In an even more unusual approach, the impersonator offered to send Hung a brand-new Samsung smartphone and arranged for him to collect it from a convenience store in Taipei, although the delivery ultimately failed because of the store’s policies.
The case was not isolated. At least five people in Taiwan, including a city council member and a legislative aide, were contacted by someone claiming to be Yi-Shan Chen. Two were also offered new smartphones, although neither received one. A Taiwanese Ministry of Foreign Affairs official stationed in Europe was approached by another person posing as an ICIJ journalist. The sender claimed to have obtained the official’s contact information from ICIJ “headquarters” — an unusual term for a journalist to use and one that raised suspicions.
After learning that her identity had been misused, Yi-Shan Chen reported the matter to Taiwanese authorities. She said Chinese intelligence operations could exploit the credibility of investigative journalists as cover to gather information.
Fake whistleblowers target investigative reporters
The attackers did not limit themselves to impersonating journalists. They also posed as supposed whistleblowers inside China. In June 2025, an ICIJ reporter received an email from someone identifying himself as “Bai Bin,” a former judicial assistant in Beijing who claimed to possess evidence implicating China’s top anti-corruption agency in a US$10 million corruption case.
The reporter did not click the link included in the message but exchanged more than 10 emails with the sender, who eventually appeared to become frustrated. Citizen Lab said attacks like this often rely on OAuth phishing, in which victims may be directed to seemingly legitimate Microsoft or Google authorization screens and persuaded to grant access to a malicious application. Once authorized, such an application can potentially read emails, send messages, and access files, allowing extended surveillance of the account.
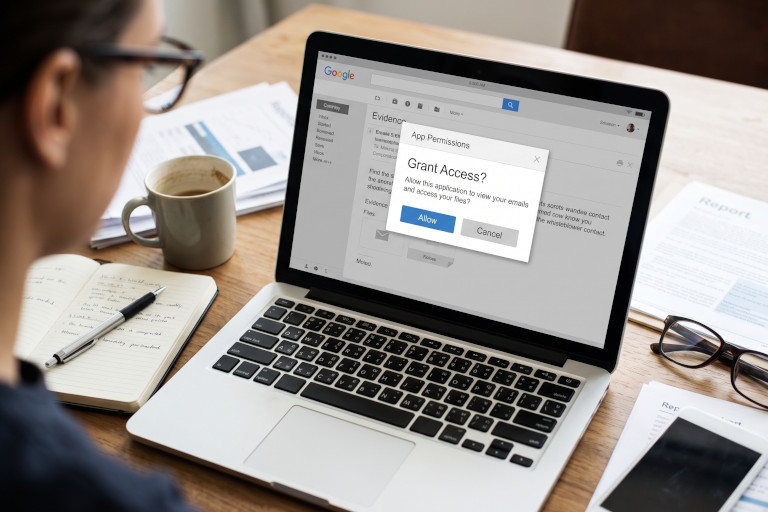
Researchers found that the attackers used more than 100 domain names in attempts to steal credentials from at least a dozen people. Some messages also contained the text “source=chatgpt.com,” suggesting that the attackers may have used artificial intelligence tools such as ChatGPT for target research or content generation. Such tools could allow attackers to produce targeted material quickly and at scale, although researchers also observed linguistic and operational mistakes.
Harassment extends beyond the ICIJ network
The campaign extended beyond ICIJ and its media partners to a broader range of overseas communities critical of the Chinese government. Citizen Lab reported that journalists covering Uyghur, Tibetan, Taiwanese, and Hong Kong issues were also targeted.
In addition to impersonating ICIJ journalists, attackers posed as film directors, members of the European Parliament, and other seemingly credible figures. They also sent fraudulent security alerts directing recipients to phishing pages.
How the attacks worked
The campaign is believed to have involved espionage activity in support of Chinese state interests, while Citizen Lab’s findings suggest some operations may have been conducted by private contractors operating within China’s commercial hacking industry. Such operators often rely on what researchers describe as “stolen narratives” — using real events, organizations, and identities to make fraudulent approaches appear credible.
Tactics identified in the campaign included:
- Creating fake ICIJ login pages
- Sending personalized messages through LINE and email
- Using OAuth phishing to steal account credentials
- Combining digital attacks with physical lures, such as offers to mail smartphones
- Using artificial intelligence to help generate large quantities of targeted content
Citizen Lab said the campaign shared similarities with previous attacks against Taiwanese semiconductor companies, suggesting that cyberespionage techniques are increasingly being incorporated into broader transnational repression operations.
A warning for press freedom and digital security
Scilla Alecci, lead reporter for ICIJ’s “China Targets” series, said the timing of the attacks likely related directly to the investigation published in April 2025. The campaign illustrates the growing risks investigative journalists face when reporting on authoritarian governments: Reporters must contend not only with efforts to obstruct their work, but also with attempts to exploit their identities and reputations to target others.
For Taiwan, such activity also threatens civil society and democratic institutions. Taiwanese authorities have increased efforts to investigate and defend against similar incidents, while the findings have raised broader concerns about the possible use of commercial hacking companies as instruments of state repression.
Citizen Lab recommends that journalists and activists use multi-factor authentication, exercise caution before clicking unfamiliar links, use secure communication tools, and remain skeptical of unsolicited gifts or supposed exclusive information. Online service providers in Taiwan have also been urged to strengthen their defenses against fraudulent accounts and phishing infrastructure.
Transnational repression moves further into the digital realm
The attacks targeting ICIJ appear to be part of a broader pattern rather than an isolated campaign. The 2025 “China Targets” investigation documented numerous examples of alleged family intimidation, physical harassment, and cyberattacks directed at critics of the Chinese government overseas. A year later, some of those tactics appear to be shifting toward more discreet, scalable, and technologically sophisticated methods.
Experts warn that protecting press freedom while defending journalists and activists from state-linked cyber threats is becoming an increasingly important international challenge. ICIJ has said it will continue its “China Targets” reporting and share security practices with its global partners. Despite the attacks, its network of investigative journalists has indicated that it does not intend to retreat from its work.
The confrontation between investigative journalists, impersonators, and cyber operators is unlikely to end soon. As digital tools become increasingly capable of disguising identities and exploiting trust, the campaign highlights how transnational repression can reach far beyond national borders and into the inboxes, accounts, and devices of those who report on it.
Translated by Eva
Follow us on X, Facebook, or Pinterest
